Skip to content

Find out where your app is vulnerable, before an attacker does.

Pentests and code review for web apps, APIs and mobile apps. Every finding comes with a concrete fix for your developers.

  • OSCP

    Certified by OffSec

  • 2 weeks

    Usually until the start, once the scope is fixed

  • NDA

    Confidentiality agreed in advance

Services

Web and API pentest

from €1,950 excl. VAT

A manual test of your web application and API, with extra depth in Laravel and WordPress.

  • Permissions and roles: who can see or do what they shouldn't
  • Login, sessions and API keys
  • Injections, SSRF and file uploads
More about the web and API pentest

Mobile pentest

from €2,250 excl. VAT

A test of your iOS and Android app, including the API behind it. With extra knowledge of React Native.

More about the mobile pentest

Security code review

from €1,520 excl. VAT

Your source code read for vulnerabilities, with the fix for each finding. Add the GDPR code check, or order it on its own.

More about the code review

No developer in house?

You have a website or web shop and want to know whether it is secure. You do not have to arrange anything technical: HackIndex sets up a safe copy, tests it and delivers a report your agency or developer can act on. If you have nobody and your site runs on WordPress, WooCommerce or Magento, HackIndex can fix it as a separate assignment.

Request a pentest

Black, grey or white box

How much you share up front decides how thorough the test is. White box gets the most out of the same testing time.

Black box

You only share the address of your app. The test starts the way an outsider without an account would.

What you provide
The URL of your app or API
Strong at
Showing what an anonymous attacker from outside can do
Good to know
A lot of testing time goes into exploring, which leaves less time for everything behind the login
Available in package
Basic

Grey box

You share test accounts per role. The test works like a logged-in user who tries to get further than intended.

What you provide
A test account per role and a short explanation of the app
Strong at
Permissions, roles and business logic
Good to know
Flaws in the code itself stay out of view
Available in package
Basic and Standard

White box

Recommended

You also share the source code and documentation. The test is combined with a look at the code, so flaws surface faster and more completely.

What you provide
Test accounts, source code and documentation
Strong at
The widest coverage in the same testing time, including flaws that are not visible from outside
Good to know
Your code is only used for this test and is covered by the NDA
Available in package
All packages

Why HackIndex

  1. Tested by hand

    Scanners find known flaws. Flaws in logic and permissions only turn up through manual testing. Every finding is verified and reproducible.

  2. Fixed price up front

    The starting prices are on the site. Once the scope is agreed you get a fixed price, with no extra charges afterwards.

  3. Fixes that fit your stack

    Every finding includes a concrete fix, written from development experience with Laravel, WordPress and React Native.

  4. Active in security research

    HackIndex researches open-source packages, reports vulnerabilities to the maintainers and publishes CVEs.

What does a pentest cost?

Starting prices for a web and API pentest. Once the scope is agreed you get a fixed price.

Basic

€1,950

from, excl. VAT

Test days
2 to 3
Suited for
Website or web shop with 1
Approach
Black, grey or
Included
Report and
Not included
APIs, and
Request a pentest
Recommended

Standard

€3,750

from, excl. VAT

Test days
5
Suited for
Web application with multiple roles and an API
Approach
Grey or
Included
Report, and 1
Not included
Request a pentest

Extended

€5,500

from, excl. VAT

Test days
7 or more
Suited for
SaaS platform, application or large API
Approach
Included
Report, and 1
Not included
Request a pentest

Mobile pentest from €2,250

Security code review from €1,520

GDPR code check from €1,150

About black, grey and white box

Research

HackIndex researches open-source packages for vulnerabilities and reports them to the maintainers.

Research
Status Vulnerability Package Severity CVE Published
Published Unsafe deserialization in statamic/importer CWE-502 statamic/importer High Not yet 12 Nov 2026
Published Access control not enforced in ai-openrouter-gateway CWE-862 andrecorugda/ai-openrouter-gateway High Not yet 7 Nov 2026
Published Stored XSS in parallax/filament-comments CWE-79 parallax/filament-comments Critical CVE-2026-90943 14 Sep 2026
Published Hidden spyware and adware in the ModHeader browser extension Chrome Web Store en Edge Add-ons ModHeader - Modify HTTP headers High Not yet 12 Jul 2026
In triage Inefficient regular expression CWE-1333 Hidden until publication High Not yet Not yet
In triage Missing authorization CWE-862 Hidden until publication Critical Not yet Not yet

Package names and dates stay hidden until the maintainer has released a fix. That keeps users of those packages protected.

How it works

Everything can be done by email. The test starts by arrangement, usually within two weeks of the scope being fixed. No test environment? HackIndex sets one up for you.

  1. Intake

    By email or in a short call: what needs testing, why and when.

  2. Scope

    The test is scoped. A fixed price follows.

  3. Agreements

    NDA, written permission and access to the test environment, or to your hosting when HackIndex sets it up.

  4. Test

    Manual, with tools as an aid, in the evenings and at weekends. Critical findings are reported straight away.

  5. Report

    Within 10 working days of the test, with the evidence and the fix for each finding, followed by a debrief.

  6. Retest

    Optional: once fixed, every finding is tested again. Included from Standard.

More about the approach

The report

What a report looks like

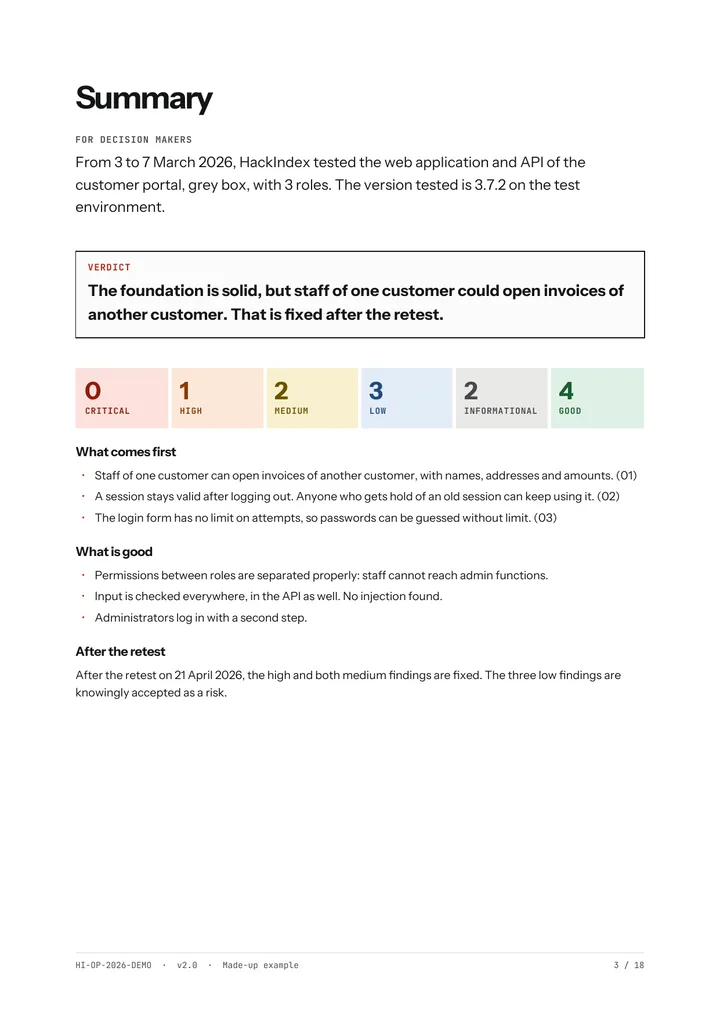
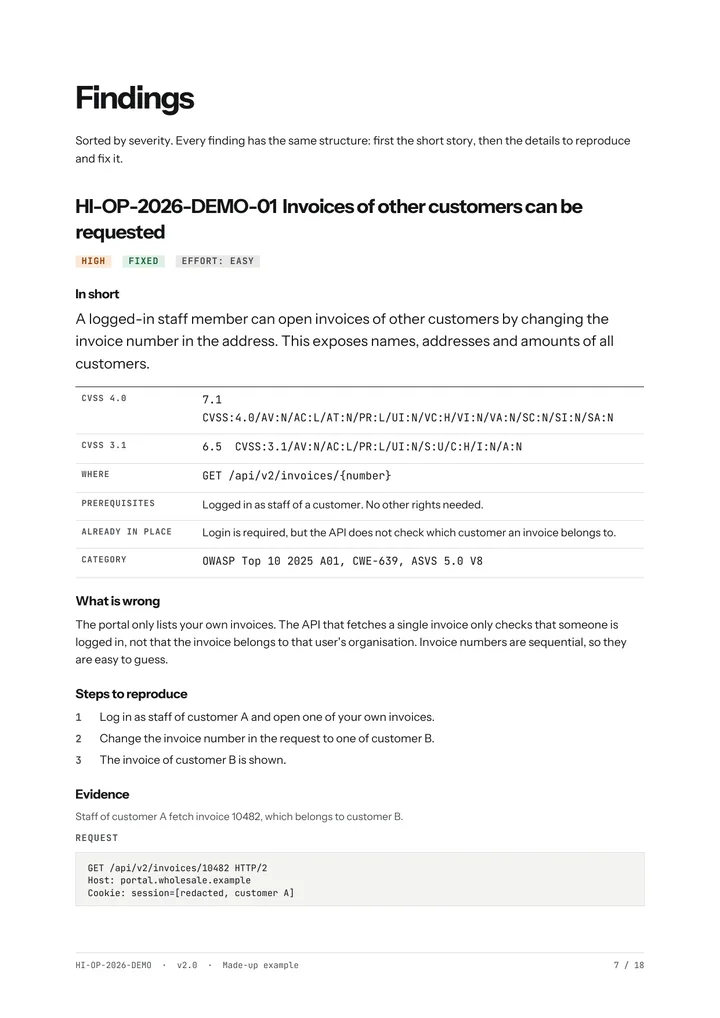
A made-up example: the customer portal of a wholesaler, with 1 high, 2 medium and 3 low findings, and the retest included.

Pages from the HackIndex sample report
View the sample report
  1. One-page summary A verdict, the findings by severity and what comes first. For decision makers.
  2. For each finding Severity with CVSS, evidence, impact and a fix that fits your code.
  3. What was not tested With the reason, so you know where the limits are.
  4. Retest The status of each finding after fixing, in the same report.

View the sample report An 18-page PDF, with made-up data.

Frequently asked questions

What does a pentest cost?

A web and API pentest starts at €1,950 excl. VAT for a website or web shop. More roles, more endpoints or a larger application make the test bigger. Once the scope is agreed you get a fixed price.

What is the difference between a scan and a pentest?

A scan looks automatically for known flaws. A pentest searches by hand for flaws in logic, permissions and integrations that a scanner misses.

Do I need to call first?

No, everything can be done by email. Sometimes a short call helps to sharpen the scope. It is then scheduled together.

How soon can a test start?

By arrangement, usually within two weeks of the scope being fixed. No test environment? HackIndex sets one up.

How soon do I get a reply?

Within 2 working days of your request. The report follows within 10 working days of the test.

What do I need to provide?

A test account per role and a fixed point of contact. No test environment? Then access to your hosting or a backup is enough, HackIndex sets up the copy. For white box also the source code and documentation.

I know little about tech. Can I still have a test done?

Yes. You need no test environment or technical knowledge. HackIndex comes from software development and sets up a safe copy of your site itself, so your live site runs no risk. For common sites, such as WordPress, WooCommerce and Laravel, at no extra cost.

Who fixes the findings?

Your own developer or agency: the report is written for that, with a fix for each finding. If you have nobody, HackIndex can fix them as a separate assignment at extra cost, for apps in Laravel, WordPress, WooCommerce, Magento, another PHP framework, Node.js or Python.

What happens if something critical is found?

Critical findings are reported right away, not only in the report. That way you can act immediately.

What happens to my data?

Confidentiality is agreed in advance in an NDA. Reports are shared encrypted.

Get your app tested.

Briefly describe what needs testing. You'll receive a proposal with a fixed price.