

Your client asks for a pentest. HackIndex does it for you.
HackIndex tests the websites and apps you build. The report is in your client's name or white label in your agency's name, with a fix for each finding that your developers can apply straight away.
- White label or in your client's name
- A fixed price you can pass on
- Fixes for your developers
When
When agencies bring in HackIndex
-
A client demands a pentest report
For example for their own audit or for their customers. You deliver the report without testing yourself.
-
A tender asks for it
A recent pentest is then often a requirement to take part.
-
Something big goes live
Test a new module, payment flow or API before real users can reach it.
-
You take over a codebase
Know what you take on before you are responsible for it.
Three parties
Who does what
A test through an agency has three parties. The agreements are set before anything is tested.
-
You The agency
- Requests the test and gets a fixed price
- Chooses: report in the client's name or white label
- Fixes the findings, or has HackIndex do it
-
Your client The owner
- Gives written permission for the test
- Even when you place the order
- Gets a statement for their auditor on request
-
HackIndex The tester
- Signs the NDA before anything is shared
- Only tests within the scope and test window
- Delivers report, debrief and retest
For your developers
What your developers get
Written for the people who fix it, with extra depth in Laravel, WordPress and React Native.
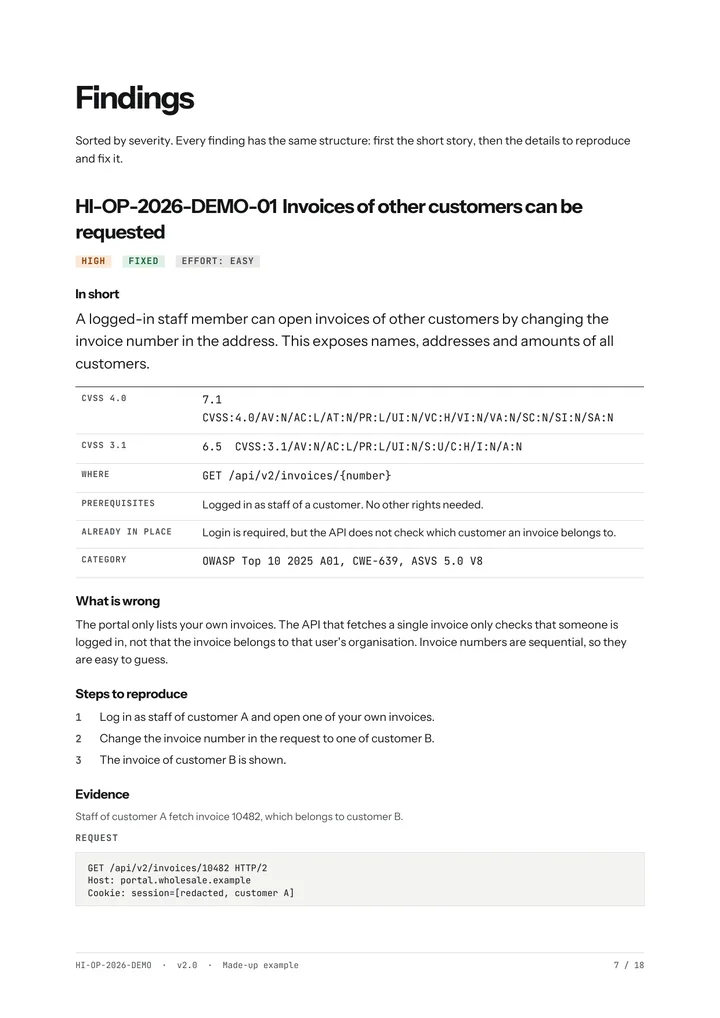
- For each finding The evidence, the impact and a fix that suits your client's stack.
- Debrief The findings walked through with your team, so everyone knows what comes first.
- Retest Once fixed, every finding is tested again, with the status of each finding in the report.
- Statement for the auditor On request a one-page statement, without findings, for your client.
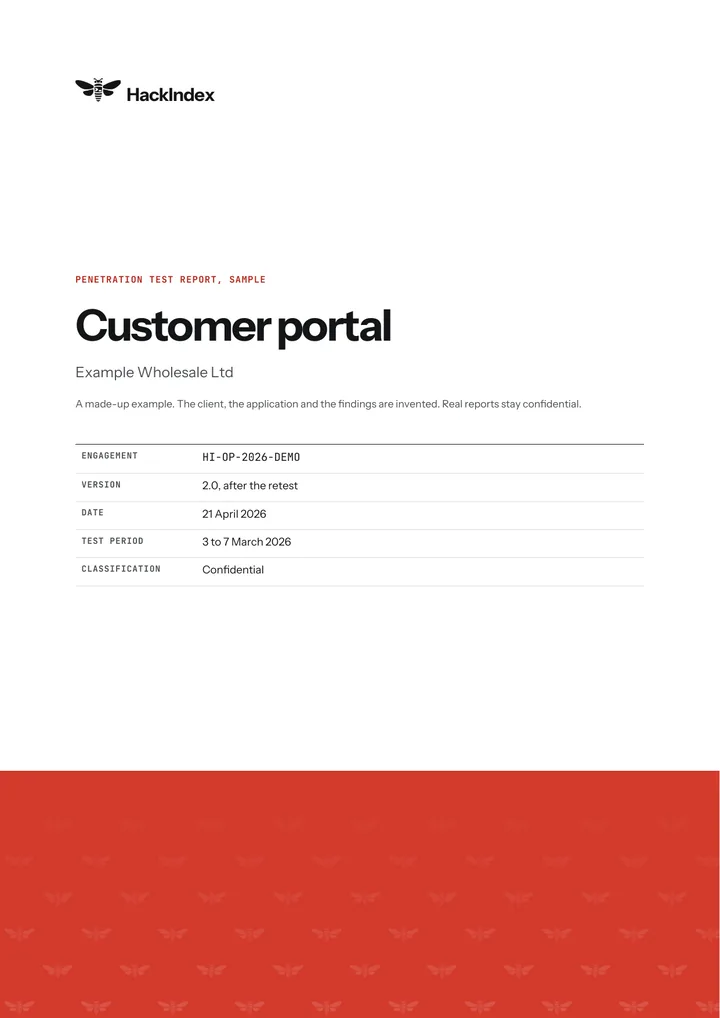
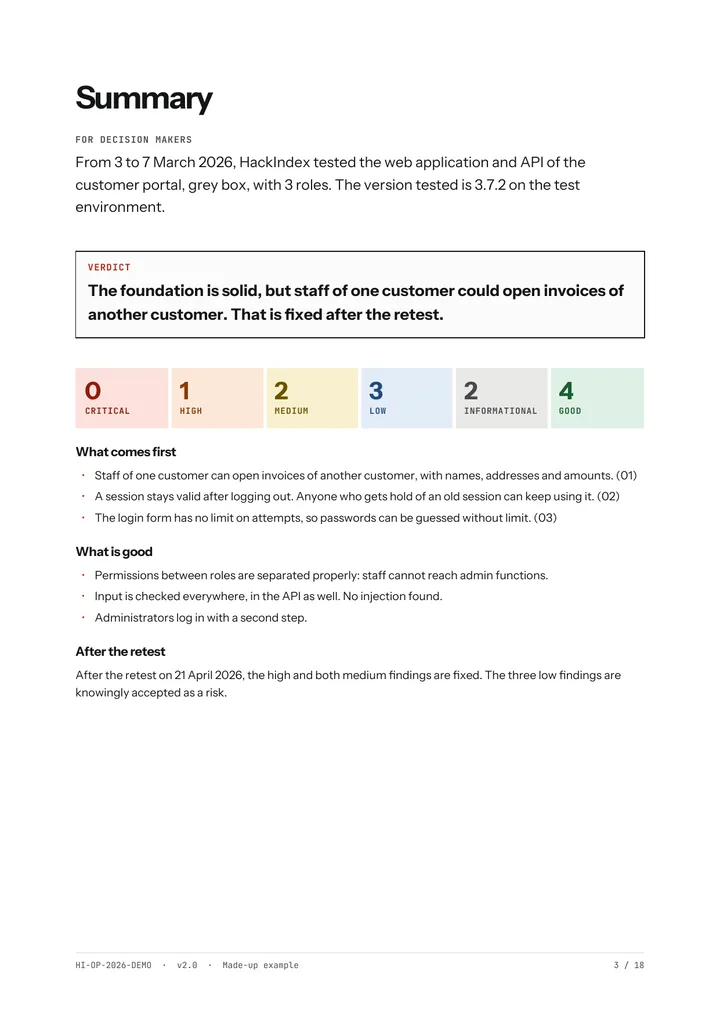
View the sample report An 18-page PDF, with made-up data.
What you can have tested
- Web and API pentest Web apps, portals and APIs, with extra depth in Laravel and WordPress from €1,950 excl. VAT
- Mobile pentest iOS and Android apps, including the API behind them from €2,250 excl. VAT
- Security code review Your client's source code read for vulnerabilities from €1,520 excl. VAT
- GDPR code check How the code handles personal data from €1,150 excl. VAT
Several clients or a fixed arrangement
Building for several clients? Ask about an arrangement for several sites, or a yearly test with a price agreed together. That way you do not have to arrange it again for every project.
Request a pentestFrequently asked questions
Can the report be in my agency's name?
Yes, white label. Or in your client's name. You choose when you request it.
Can I include the pentest in my own quote?
Yes. Once the scope is agreed you get a fixed price, which you can pass on.
Who gives permission for the test?
The owner of the application, in writing. Even when you place the order.
Do you fix the findings too?
The report is written for your developers. If you lack the capacity, HackIndex can fix them as a separate assignment at extra cost, for apps in Laravel, WordPress, WooCommerce, Magento, another PHP framework, Node.js or Python.
Get your client's app tested.
Tell which client and what needs testing. You get a proposal with a fixed price.